FIPS 140-3 validated communications
Enable optional FIPS 140-3 validated cryptography for in-scope Agent-to-platform and supported Web Remote communications. Available through Restricted Access, the capability uses NIST-validated Kaseya cryptographic modules across supported Windows, macOS and Linux devices and can be enabled or disabled at the account level through Global Settings.
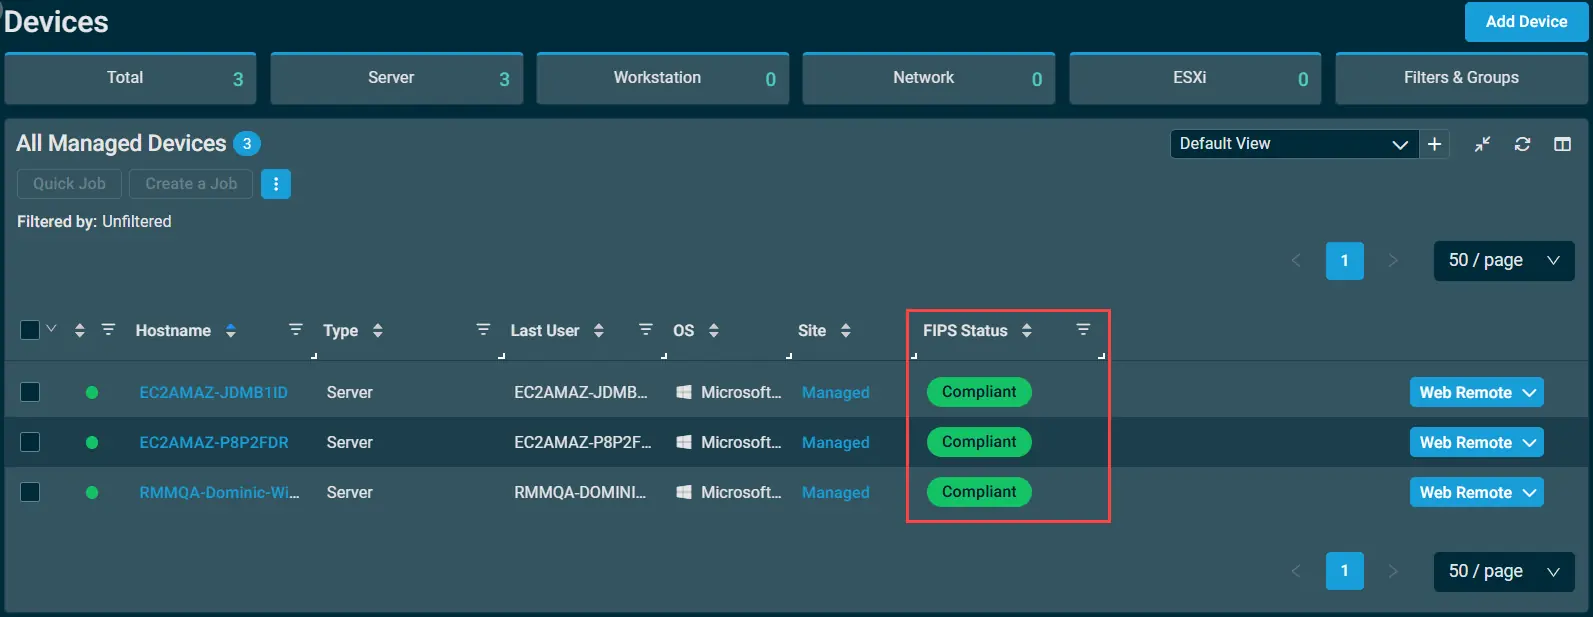
Administrators can monitor adoption through device-level Compliant, Non-Compliant, and Unsupported OS statuses, dedicated filters and a FIPS Compliance Summary dashboard widget. Devices unable to use the validated cryptographic module remain connected through the standard secure communication mechanism and are identified as Non-Compliant, helping IT teams investigate exceptions without disrupting device management. Supported Web Remote sessions also display session compliance information and record non-FIPS activity in the Activity Log.
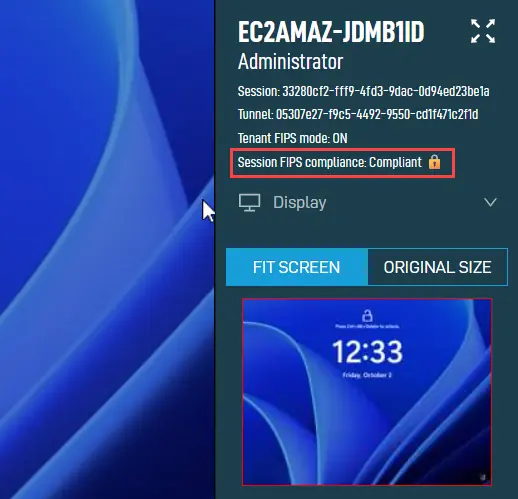
Release status: Restricted Access. Participation is by invitation.
One Complete Platform for IT & Security Management
Kaseya 365 is the all-in-one solution for managing, securing, and automating IT. With seamless integrations across critical IT functions, it simplifies operations, strengthens security, and boosts efficiency.
MCP vs. API: What’s the difference and why it matters
Explore the differences between MCP and APIs, how MCP builds on APIs like the Datto RMM API, and when IT teams and MSPs should use each approach or both.
Read now
What is an MCP server? A guide for MSPs
An MCP server connects the AI tools you already use to your RMM, PSA and documentation platforms. Learn how MCP works, what MSPs gain and how to secure it.
Read now